

The New Role of AI in Cybersecurity Defense
In today’s digital world, cyber threats evolve faster than ever. Traditional, rule-based security systems, signature detection, firewalls, and static rules can no longer keep pace with the speed, scale, and sophistication of modern attacks. This is where Artificial Intelligence (AI) comes into play.
AI is no longer a futuristic add-on; it has become the backbone of modern cybersecurity defense. From spotting zero-day malware to detecting subtle insider threats, AI-driven solutions are proving their worth and raising the bar for what it means to be “secure.”
In this article, we explore how AI is reshaping cybersecurity: the techniques behind it, real-world use cases, benefits, challenges, and concrete recommendations for organizations that want to stay ahead of the threat curve.
Why Traditional Cybersecurity Is No Longer Enough
Before diving into AI’s role, it’s worth understanding why conventional security struggles today:
- Volume & velocity of data: Modern organizations generate massive amounts of logs, network traffic, user events, endpoint data, and cloud-native telemetry. Human analysts simply can’t keep up.
- Evolving attack sophistication: Threat actors now employ polymorphic malware, AI-assisted phishing, stealthy lateral movement, automated reconnaissance, many designed to evade static detection.
- Expanding attack surface: With cloud adoption, remote work, IoT, edge computing, and hybrid environments, the “perimeter” of security is fluid and complex.
- Delayed reaction time: Static defenses often react only after attacks are detected, leaving a window for damage.
Given these challenges, cybersecurity demands adaptive, intelligent, and scalable solutions. Enter AI.
What AI Brings to Cybersecurity: Core Capabilities
At its core, AI enhances cybersecurity by bringing:
- Pattern recognition at scale, analyzing massive datasets (network logs, user behavior, telemetry) to detect anomalies or suspicious patterns
- Automation and speed enable real-time detection and response, 24×7, far beyond human capacity.
- Learning and adaptation of machine learning (ML) models improve over time, adapting to new attack vectors and threat evolutions.
- Predictive and proactive defense forecasting potential threats before they materialize, enabling pre-emptive measures.
- Behavioral and context-aware analysis goes beyond signatures, focusing on context (user behavior, device state, environment) to detect subtle threats like insider risk or reconnaissance.
Let’s see how these play out in real-world applications.
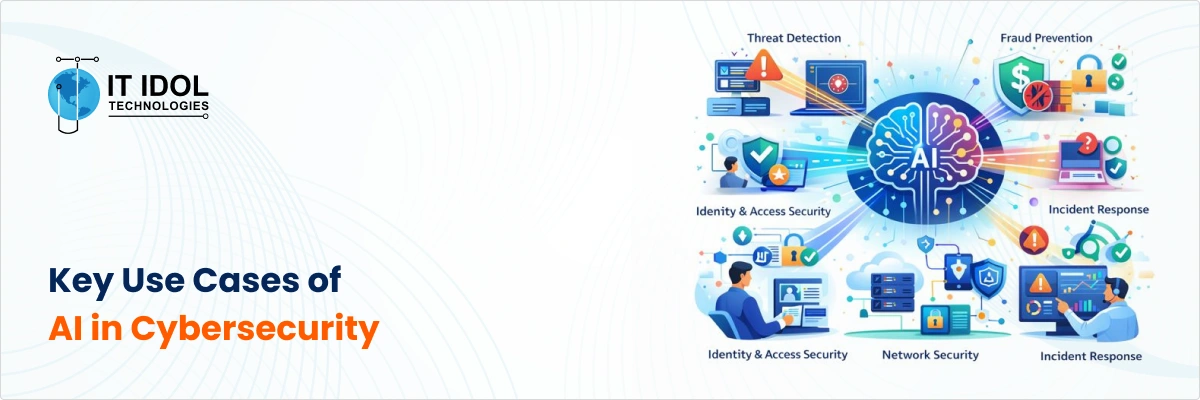
Key Use Cases of AI in Cybersecurity
Anomaly Detection & Real-Time Threat Hunting
One of the most powerful applications of AI is in anomaly detection, i.e., identifying behavior or events that deviate from established baselines. This can detect previously unknown (zero-day) threats, insider threats, or subtle reconnaissance activity.
- A 2025 survey found that over 60% of cybersecurity companies now embed ML-based anomaly detection in their defense stack.
- Recent academic work demonstrates that “lightweight and explainable” AI models can perform real-time threat detection even in resource-constrained environments such as edge systems, balancing performance with interpretability.
Takeaway: AI enables detection of threats that traditional signature-based tools miss, especially “unknown unknowns.”
Malware & Intrusion Detection
Traditional antivirus or intrusion-detection systems often rely on known signatures. AI takes this further by using ML/deep learning to classify malware, detect suspicious behaviour, and unearth novel attack patterns.
- A comprehensive 2025 industry review concluded that AI/ML-based intrusion detection, behavioral analysis, and malware classification now outperform many legacy systems.
- Research into adversarial-defense techniques, e.g., using generative-adversarial networks (GANs), is pushing the frontier, reinforcing AI’s role not just in detection, but in resilience against adversarial attacks.
Takeaway: Organizations can use AI to detect and block malware or intrusion attempts faster, even when attackers use novel or obfuscated techniques.
Threat Intelligence & Predictive Analytics
AI isn’t just reactive, it’s becoming predictive and proactive. By ingesting threat-intelligence feeds, analyzing global attack patterns, and correlating data across sources, AI can forecast likely threat vectors, emerging vulnerabilities, and potential breaches.
- According to recent data, about 40% of AI-based cybersecurity tools integrate threat-intelligence feeds, enabling a broader, real-time view across networks and external threats.
- As AI systems grow smarter, many cybersecurity vendors are positioning them as central to future security frameworks, not as optional add-ons.
Takeaway: AI-driven threat intelligence enables organizations to anticipate and prepare for threats, shifting from reactive to strategic defense.
Automation of Security Operations & Incident Response
One of the biggest benefits for busy security teams: automation. AI-driven tools can triage alerts, prioritize incidents, correlate events, and often respond in real-time, reducing manual workload and cutting response time.
- Industry data suggests AI security systems can automate up to 75% of cybersecurity operations in some organizations.
- Automation has reportedly reduced the detection time of malware or intrusion dramatically, sometimes by 60% or more compared to traditional methods.
Takeaway: AI helps scale security operations, letting human experts focus on the most complex threats and respond faster.
Real-World Impact: Adoption, Results & ROI
Understanding theory is one thing; seeing concrete outcomes is another. Here’s what recent data shows about real-world impact and adoption of AI in cybersecurity.
| Metric / Insight | Data Point / Trend |
| Adoption by firms | ~80% of cybersecurity firms report investing in AI to improve threat detection capabilities. |
| Improved detection & response | AI-based malware detection systems have reduced detection times by ~60%. |
| Efficiency gains in SOC | Many organizations claim AI has made their Security Operations Center (SOC) more efficient, speeding up incident response and reducing false positives. |
| Business confidence | Over 70% of enterprise security leaders view AI as essential to their security strategy. |
| Market growth | The global AI-in-cybersecurity market is projected to reach tens of billions of dollars in the coming years. |
These findings underscore a powerful reality: AI isn’t just hype. It’s delivering measurable value, faster detection, fewer false positives, better efficiency, and improved security posture.
Takeaway: For many companies, AI has shifted from “nice-to-have” to “must-have.”
Source: mckinsey.com
Emerging Trends: What’s New (2024–2025)
AI in cybersecurity is not static; it evolves rapidly. Here are some of the most important recent trends:
1. Lightweight & Explainable AI for Edge and IoT Environments
As more IoT, edge, and mobile devices join corporate networks, traditional heavy-duty AI becomes impractical for constrained devices. Recent research (2025) highlights “lightweight and explainable” AI models that can run on edge devices, enabling real-time threat detection without sacrificing performance or interpretability.
Implication: Organizations expanding into edge, IoT, remote work, or hybrid infrastructure can still deploy AI defense without needing powerful servers or GPUs everywhere.
2. GAN-Based Defenses & Adversarial-Resilient Models
With attackers themselves increasingly using AI, including adversarial ML or generative techniques, defensive AI must evolve. Emerging work on GAN-based defenses seeks to detect adversarial inputs, obscure exploit attempts, and harden ML-based security tools against manipulation.
Implication: Organizations should anticipate that threat actors will evolve and choose AI tools that are designed to resist AI-driven attacks.
3. AI-Driven Threat Intelligence & Unified Monitoring Platforms
Rather than isolated point tools, cybersecurity platforms are increasingly integrating AI-driven threat intelligence, global telemetry feeds, anomaly detection, and automated response, forming unified, intelligent security ecosystems.
Implication: Security strategy is shifting from fragmented tools to holistic, AI-powered platforms; future-ready organizations will likely standardize around such unified systems.
4. Growing Adoption, But Realistic Caution
While adoption is rising, some organizations remain cautious. Deployment isn’t always simple: there are concerns around data privacy, compliance, skills shortage, maintenance overhead, and over-reliance on AI.
Implication: AI should not replace human oversight but augment it. Successful deployment depends on governance, skilled personnel, and proper integration.
Challenges & Risks of AI-Driven Cybersecurity
No technology, however powerful, is a silver bullet. AI-based cyber defense brings significant benefits but also comes with its own risks and limitations.
Skill Shortage and Talent Gap
Deploying and managing AI-powered security tools requires expertise in ML/AI, data science, cybersecurity, and operations. Many organizations struggle to find or train such talent.
Risk: Misconfigured models, lack of tuning, or weak monitoring may lead to failures or worse, a false sense of security.
Recommendation: Invest in training; consider hybrid teams combining security analysts and data/ML specialists; or leverage managed-security providers with AI expertise.
Data Quality, Privacy & Compliance
AI models require vast amounts of data logs, telemetry, user behavior, and network traffic. Poor data quality, bias, missing context, or inadequate anonymization can lead to false positives, false negatives, or privacy breaches.
Risk: Overlooked threats, privacy violations, and regulatory non-compliance.
Recommendation: Establish robust data governance; anonymize or pseudonymize sensitive data; ensure compliance with local/international regulations; regularly audit data pipelines.
Over-Reliance and Reduced Human Oversight
Automated systems can cause organizations to become complacent. If security teams lean too heavily on AI, novel or subtle threats not recognized by the model may slip through.
Risk: Blind spots, missed threats, inability to adapt.
Recommendation: Maintain human-in-the-loop oversight. AI should assist analysts, not replace them. Encourage human review, model audits, and manual threat-hunting.
Computational Cost & Maintenance Complexity
Advanced AI techniques, especially deep learning, require computational resources (GPUs, servers), ongoing retraining, and maintenance. For many organizations (especially SMEs), this can be a non-trivial overhead.
Risk: High costs, performance bottlenecks, inconsistent detection.
Recommendation: Use lightweight or hybrid models where possible; consider cloud-based AI security solutions; weigh cost vs ROI carefully before wide deployment.
How to Adopt AI in Cybersecurity? A Strategic Framework
For organizations looking to embrace AI-based defense, the following strategic roadmap can help ensure success:
1. Start with a Gap Analysis
- Inventory existing security controls, tools, and processes.
- Identify key pain points: high alert volume, slow response time, blind spots, insider threats, cloud/IoT expansion, etc.
- Determine what your risk tolerance is and which classes of threats you most need to address.
2. Define Objectives & Use Cases Clearly
Decide why you want AI: faster detection? Improved threat intelligence? Insider threat monitoring? Automated response?
Avoid “AI for the sake of AI.” Focus on concrete goals.
3. Choose the Right Tools / Architecture
- For edge or IoT-heavy environments → consider lightweight, explainable models.
- For enterprise-scale environments → consider cloud-native, scalable AI platforms with threat-intelligence integration.
- Evaluate vendor maturity, data governance capabilities, integration with existing SIEM/SOAR, support for manual oversight, and compliance readiness.
4. Build Skills & Governance
- Train existing security teams in AI/ML basics or recruit data-security specialists.
- Set up governance protocols: data handling, privacy, logging, auditing, human-in-the-loop for decisions, and model retraining cadence.
- Ensure ongoing monitoring and periodic review of AI systems, not “set and forget.”
5. Monitor, Measure & Iterate
- Define KPIs: detection time, false-positive rate, number of incidents caught, response time, cost savings, analyst workload, etc.
- Regularly review performance. Tune or retrain models. Adjust thresholds. Add context or additional data sources if needed.
- Stay alert to emerging threats; attackers will evolve, and so must your AI defenses.
What’s Next: The Future of AI-Powered Cyber Defense
As AI continues to evolve and attackers increasingly harness AI themselves, cybersecurity defense must keep pace. Here are some trends and directions to watch:
- Explainable AI (XAI) demand for transparency and interpretability will grow, especially for compliance, audit, and trust. Models that can explain why they flagged something will become more common.
- Adversarially Robust Models using GANs or other techniques to defend against AI-driven attacks, model poisoning, or evasion attempts.
- Unified AI Security Platforms integrating threat intelligence, anomaly detection, endpoint monitoring, cloud security, incident response, and automation under one AI-powered umbrella.
- Edge and IoT Security via Lightweight AI, as IoT and edge adoption grow, lightweight AI models optimized for constrained devices will become critical.
- Human-AI Collaboration and Augmented SOCs, rather than replace analysts, AI will augment them, handling repetitive tasks, filtering noise, surfacing insights, giving human teams time for strategic work.
Strategic Recommendations: What Every Organization Should Do Now?
If you’re leading or advising an IT or security team, here are practical, strategic moves to take:
1. Treat AI as a strategic capability, not a one-off tool: Plan budgets, training, governance, data pipelines, and integration from the outset.
2. Pilot with clear use-cases: For example, roll out AI-based anomaly detection on critical endpoints, or deploy AI-driven threat intelligence for cloud workloads.
3. Keep humans in the loop: Use AI for automation and augmentation, but ensure oversight, manual verification, and model auditing.
4. Adopt data governance and privacy safeguards first: Before feeding sensitive logs or user behavior data into AI systems, ensure compliance and anonymization standards.
5. Monitor performance, continuously refine models: Evaluate metrics; retrain models; update thresholds; integrate new data sources. Treat AI deployment as an evolving journey.
Conclusion
AI is no longer a nice-to-have innovation; it has become a strategic imperative in modern cybersecurity defense. From anomaly detection to threat intelligence to automated response, AI empowers organizations to defend at scale, adapt to evolving threats, and stay ahead of cyber adversaries.
But with great power comes responsibility. Successful adoption requires more than tools; it demands strategy, governance, human expertise, and continuous learning. In the evolving cyber battlespace, it’s not just about building smarter defenses; it’s about building resilient, adaptive, sustainable cybersecurity frameworks that evolve with the threat.
For any organization serious about cybersecurity, whether a startup, an enterprise, or a public-sector body, AI isn’t optional anymore. It’s the next baseline of defense.
TL;DR
AI has transformed cybersecurity, enabling real-time threat detection, anomaly analysis, predictive intelligence, and automated response. Organizations adopting AI report faster detection times, fewer false positives, and improved incident response efficiency. But AI isn’t a silver bullet: successful deployment hinges on skilled teams, data governance, human oversight, and ongoing model refinement. Treat AI as a strategic capability, not a one-off tool.
Also Read: The Role of AI in Reducing Tech Debt